Просмотр новости
Найдите то, что Вас интересует
 Спутники
 РН
 SpaceX
 Роскосмос
 NASA
СпутникиРНSpaceXРоскосмосNASASecurity products made by Palo Alto Networks and Cisco have been found vulnerable to active cyberattacks, raising concerns about the reliability of systems designed to protect corporate networks.The incident has also drawn scrutiny of Palo Alto, which recently promoted its experience using the advan
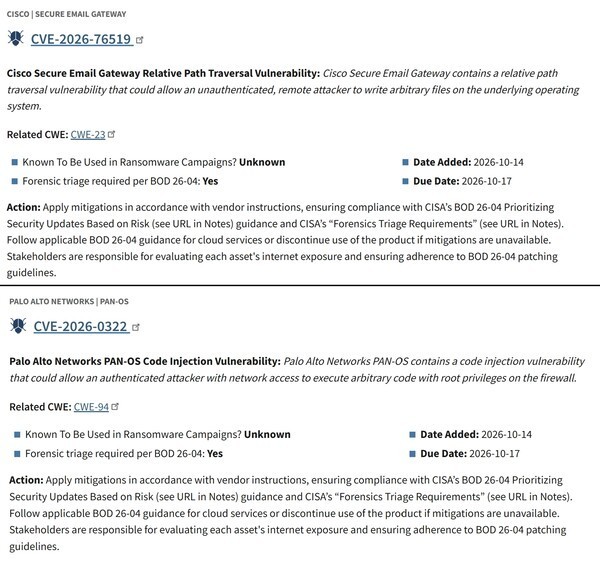
Security products made by Palo Alto Networks and Cisco have been found vulnerable to active cyberattacks, raising concerns about the reliability of systems designed to protect corporate networks.
The incident has also drawn scrutiny of Palo Alto, which recently promoted its experience using the advanced artificial intelligence (AI) model Mythos to highlight its advantages over Korean companies.
According to foreign media reports on Oct. 17, the US Cybersecurity and Infrastructure Security Agency (CISA) added vulnerabilities affecting Palo Alto firewalls and Cisco email security appliances to its Known Exploited Vulnerabilities (KEV) catalog. The agency ordered federal civilian agencies to take action by Oct. 17, local time.
The critical vulnerabilities could allow attackers to obtain root privileges and have been confirmed as exploited in actual attacks.
According to cybersecurity publication SecurityWeek, Palo Alto released a patch on Oct. 14, local time, for a PAN-OS zero-day vulnerability, CVE-2026-0322. The affected products include its PA Series physical firewalls, VM Series virtual firewalls and Panorama, a centralized management platform.
Palo Alto acknowledged observing “very limited exploitation” targeting the management interface of PAN-OS, the operating system used by these products. The management interface allows administrators to modify system settings. An attacker who can access the interface and successfully authenticate could obtain root privileges on the firewall.
Firewalls monitor communications between external networks and internal systems, blocking traffic that violates predefined security rules. Losing administrative control effectively gives attackers the keys to a system designed to prevent external intrusions.
Park Sang-kyu, head of Palo Alto Networks Korea, emphasized the company’s firewall capabilities during his keynote at Ignite on Tour Seoul 2026 on Oct. 14.
“Many companies still use L4 firewalls, but L4 firewalls cannot stop ransomware,” Park said, urging businesses to immediately upgrade to L7 next-generation firewalls, Palo Alto’s core product category.
At Cyber Summit Korea (CSK) 2026 last month, Park also highlighted the company’s experience with advanced AI.
“It’s frightening to imagine how many vulnerabilities would be found if high-performance frontier AI scanned the software and networks of Korean institutions and companies,” he said, adding that such work should be handled by experienced specialists.
His remarks suggested that organizations should rely on Palo Alto’s expertise in using advanced AI models such as Mythos.
Palo Alto Networks Korea attracted attention last year when it became the first foreign vendor to supply a security monitoring system to the Bank of Korea. The company has reportedly been reorganizing its sales operations to expand into Korea’s public sector market. The latest security incident is expected to complicate that strategy.
Meanwhile, Cisco acknowledged that a vulnerability in the Advanced Malware Protection (AMP) feature of its Secure Email Gateway, CVE-2026-76519, was being actively exploited. AMP is designed to scan email attachments. The vulnerability received a severity score of 9.8 out of 10 under the Common Vulnerability Scoring System (CVSS).
Attackers could send an email containing a specially crafted attachment to write arbitrary files to the appliance’s operating system and execute commands with root privileges.
Attackers with root access could also delete or conceal evidence of compromise. Cisco therefore advised customers to inspect external network and firewall logs for suspicious activity.
| # | Наименование новости | Тональность | Информативность | Дата публикации |
|---|---|---|---|---|
| 1 | «Дыра», которую прежде считали мелкой, делает файерволлы бесполезными | -2 | 8 | 19-06-2026 |
| 2 | «Дыра», которую прежде считали мелкой, делает файерволлы бесполезными | -2 | 7 | 19-06-2026 |
| 3 | Cisco warnt vor Attacken auf Secure Firewall Adaptive Security Appliance | 0 | 5.34 | 12-08-2026 |
| 4 | Spy agencies say AI can help combat AI cyber risks. But don’t forget the basics | 0 | 6 | 24-06-2026 |
| 5 | Palo Alto Networks: Zahlreiche Sicherheitslücken in Prisma Browser geschlossen | 0 | 10.42 | 13-08-2026 |
| 6 | PAN-OS: Schadcode schlüpft durch Root-Lücke in Palo-Alto-Firewalls | 0 | 30 | 15-10-2026 |
| 7 | WSJ: кибератаки в США коснулись Cisco, Intel, NVidia и других | 0 | 0 | 21-12-2020 |
| 8 | Falhas em VPN expõem empresas a ransomware | 0 | 6.53 | 28-07-2026 |
| 9 | Cyberangriffe auf F5 BIG-IP, Check Point Security und Arista VeloCloud | 0 | 15 | 23-09-2026 |